San Francisco × Singapore / founded 2023

A cyber frontier lab with an operator’s perspective.

We build the agents and cyber models that help enterprises find weaknesses, prove what an attacker could do and move the fix into engineering. Our roots are in protecting real platforms, understanding adversaries and building security systems.

Our mission

Make offensive security a continuous discipline.

Move offensive security from point-in-time assessments to continuous testing, using cyber-specific models and agentic capabilities.

Software changes every day. AI agents gain new tools, applications gain new users and a release can change an attack path. Security teams need a way to test those changes and see which weaknesses matter.

FailSafe connects research with the work of the people responsible for the system. We build threat models, test the authorized scope, reproduce findings and help engineers act on the evidence. Human teams retain control over access, approvals and deployment.

How our agentic approach works

Our roots

A company built around security, research and product engineering.

Founded in February 2023, FailSafe brings together leadership across enterprise security, research, engineering and product. That experience informs how we think about adversaries, evidence and the operational cost of security failures.

San Francisco and Singapore connect our research and engineering work with enterprise teams across Asia-Pacific and beyond. We serve financial institutions, critical infrastructure, technology companies and other organizations where a security finding needs to become a decision someone can act on.

Backed by

Sequoia · Dragonfly Capital · Grab Ventures

We build for the security teams and engineers responsible for the systems their organizations depend on.
The founding team

Built by operators, cryptographers and product engineers.

Experience protecting large platforms, studying security protocols and operating in adversarial environments shapes how we build FailSafe.

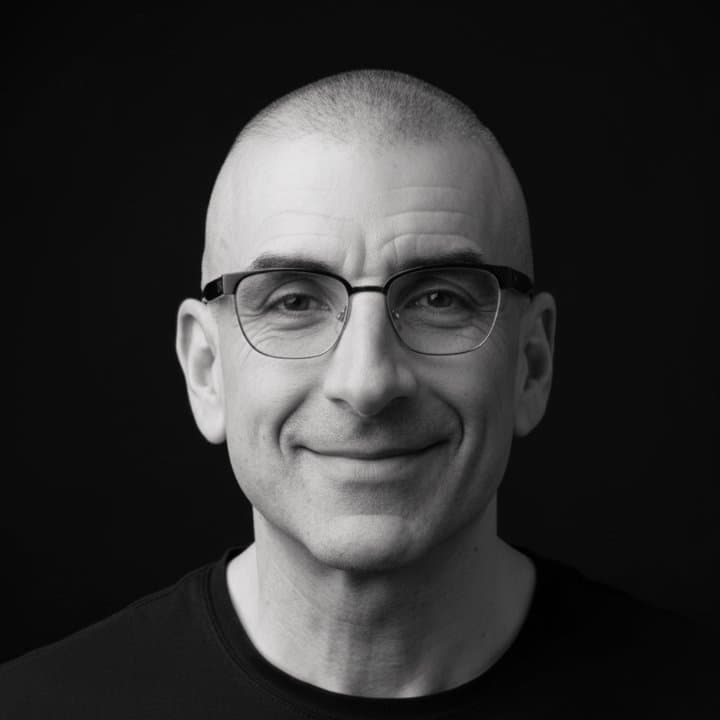
Aneirin Flynn

Aneirin Flynn

Co-founder & CEO

Military and naval operations

A former naval officer with a background in military operations and intelligence analysis. Aneirin brings an adversarial perspective to FailSafe’s work on autonomous testing, operational control and sovereignty for sensitive environments.

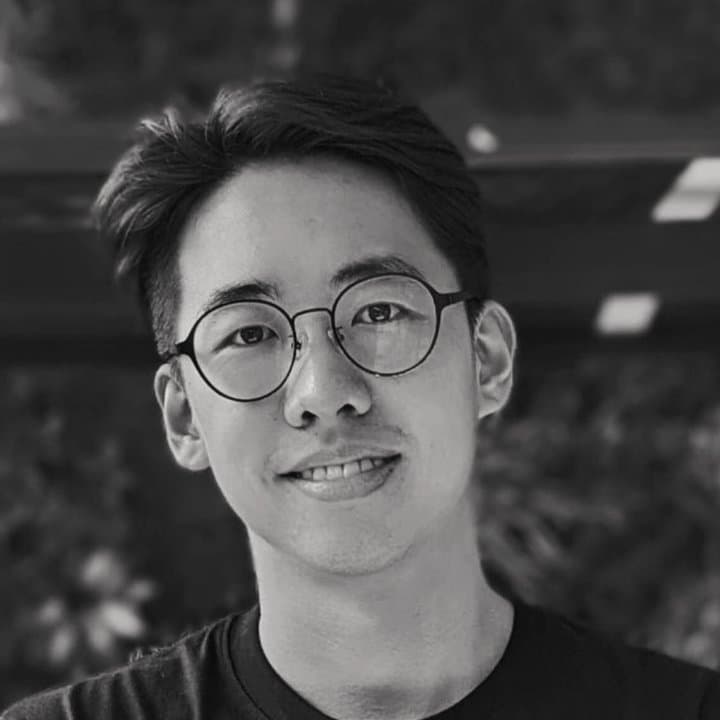
Wui Foo

Wui Foo

Co-founder & President

Founding CISO of Grab; previously Google

Grab’s founding chief information security officer from 2015 to 2022. Earlier at Google, Wui worked on protecting YouTube, Google Search and social products. He brings the operator’s experience of protecting large consumer platforms to FailSafe’s enterprise security work.

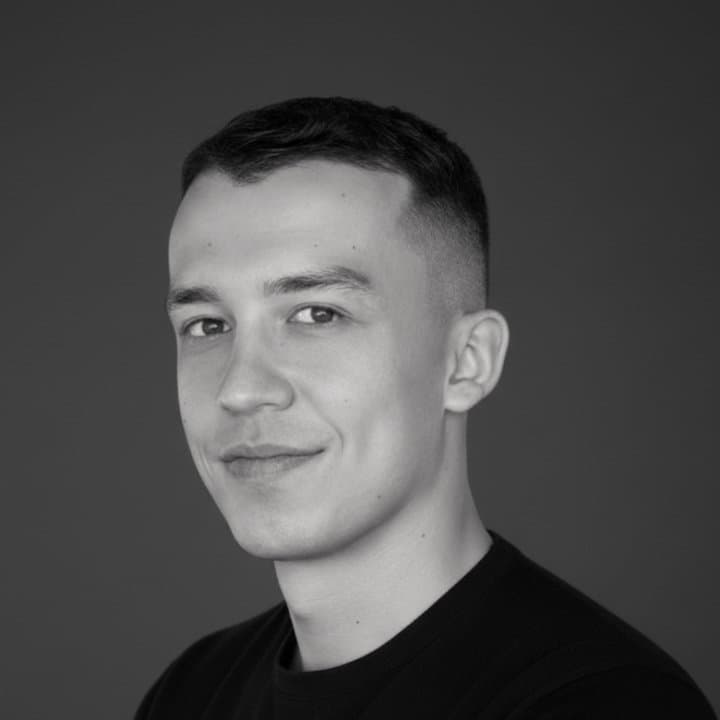
Ari Medvinsky, PhD

Ari Medvinsky, PhD

Co-founder & CTO

Applied cryptography, identity and security

A cryptographer and DARPA Scholar with 30 years of experience across Okta, Google and Microsoft. Ari leads FailSafe’s technical direction, connecting security research, cyber models and evidence-based testing. He is a co-author of RFC 2712, which added Kerberos cipher suites to TLS.

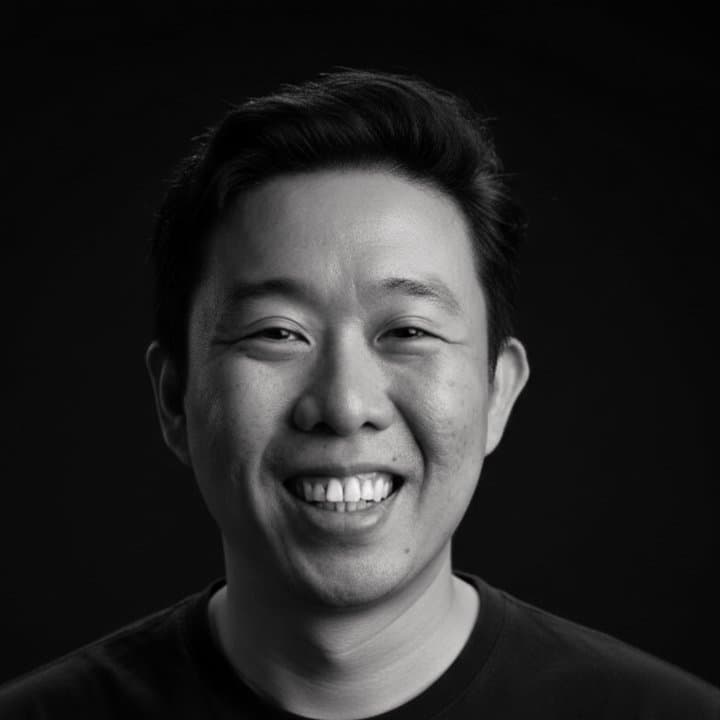
Henry Foo

Henry Foo

Co-founder & CPO

Product engineering; previously Micron

A former product engineer at Micron with experience in low-level chip design. Henry leads product at FailSafe, shaping how security teams use SWARM to identify weaknesses, inspect validated evidence and move findings into remediation.

Read Ari’s protocol research in RFC 2712.

Research that becomes a product

One lab. Connected security work.

SWARM

Agentic testing that connects threat modeling, reproduced findings and remediation workflows across your agreed application, network and AI-system scope.

Explore the platform

HIVE

Agentic red teaming of mission logic and software control planes for OT, robotics, embodied AI and autonomous fleets.

Explore HIVE

COCOON

Cryptographic trust and post-quantum resilience assessment within FailSafe’s offensive-security practice.

Explore COCOON

GlassBreak

Our security-post-trained cyber models and the execution workflows around them, with private inference options for sensitive enterprise work.

Meet our cyber models

Published research

Versioned benchmark results and coordinated vulnerability disclosures. Read the method and evidence behind a result, including its limits.

Inspect the evidence

For sensitive workloads, own your hosting and inference. For public company details, visit our company facts.

How we work

Show the evidence. Respect the boundary. Follow through.

Evidence over assertion

A finding should explain what happened, why it matters and how an engineer can reproduce it. Published research should identify its method and limitations.

Operational responsibility

Testing starts with authorization and an agreed scope. Sensitive data, model processing and access controls are part of the deployment design.

Research that ships

Useful research improves a model, an assessment or an engineering workflow. We work toward results a security team can use.

Build with us

Work on the security problems AI creates.

Join our researchers, engineers and operators in building agentic security testing. Or bring us the enterprise problem your team needs to solve.

Questions & answers

Frequently asked questions

Our mission, founding team, locations and security work.

FailSafe is a cyber frontier lab building agentic penetration testing and continuous offensive security. SWARM identifies weaknesses, validates exploitability and helps engineering teams remediate. GlassBreak is our cyber-model research and development program.

FailSafe was founded in February 2023. Its co-founders lead company strategy, enterprise security, technical development and product.

FailSafe operates from San Francisco and Singapore, connecting Bay Area engineering and research with enterprise security work across Asia-Pacific. Further company presence includes London, Tokyo and Sydney.

FailSafe’s co-founders are Aneirin Flynn, CEO; Wui Foo, President; Ari Medvinsky, PhD, CTO; and Henry Foo, CPO. They lead the company’s security, research, engineering and product work.

Move offensive security from point-in-time assessments to continuous testing, using cyber-specific models and agentic capabilities.

FailSafe works with regulated financial institutions, critical infrastructure operators, consumer technology and fintech companies, government-linked organizations and enterprises in sectors including retail, property and manufacturing. Public research disclosures are distinct from commercial customer relationships.

Current roles and application instructions are listed on the careers page. Roles span engineering, applied AI, customer deployment and security partnerships. Location and travel requirements are specified for each opening.